


Free 350-701 Sample Questions and 100% Cover Real Exam Questions (Updated 607 Questions)
Download Real Cisco 350-701 Exam Dumps Test Engine Exam Questions
The Cisco 350-701 or Implementing and Operating Cisco Security Core Technologies is a core exam that’s related to the CCNP Security, Cisco Certified Specialist-Security Core, and CCIE Security certifications. From the name, this test checks your knowledge and skills regarding the execution and operations necessary for basic security technologies.
NEW QUESTION # 47
What are two functionalities of northbound and southbound APIs within Cisco SDN architecture? (Choose two.)
- A. Southbound APIs utilize CLI, SNMP, and RESTCONF.
- B. Northbound interfaces utilize OpenFlow and OpFlex to integrate with network devices.
- C. Southbound APIs are used to define how SDN controllers integrate with applications.
- D. Northbound APIs utilize RESTful API methods such as GET, POST, and DELETE.
- E. Southbound interfaces utilize device configurations such as VLANs and IP addresses.
Answer: A,E
NEW QUESTION # 48
Which two deployment modes does the Cisco ASA FirePower module support? (Choose two)
- A. passive monitor-only mode
- B. routed mode
- C. inline mode
- D. transparent mode
- E. active mode
Answer: C,E
Explanation:
You can configure your ASA FirePOWER module using one of the following deployment models: You can configure your ASA FirePOWER module in either an inline or a monitor-only (inline tap or passive) deployment. Reference: https://www.cisco.com/c/en/us/td/docs/security/asa/asa92/asdm72/firewall/asa-firewall-asdm/ modules-sfr.html You can configure your ASA FirePOWER module in either an inline or a monitor-only (inline tap or passive) deployment.
Reference:
You can configure your ASA FirePOWER module using one of the following deployment models: You can configure your ASA FirePOWER module in either an inline or a monitor-only (inline tap or passive) deployment. Reference: https://www.cisco.com/c/en/us/td/docs/security/asa/asa92/asdm72/firewall/asa-firewall-asdm/ modules-sfr.html
NEW QUESTION # 49
Refer to the exhibit.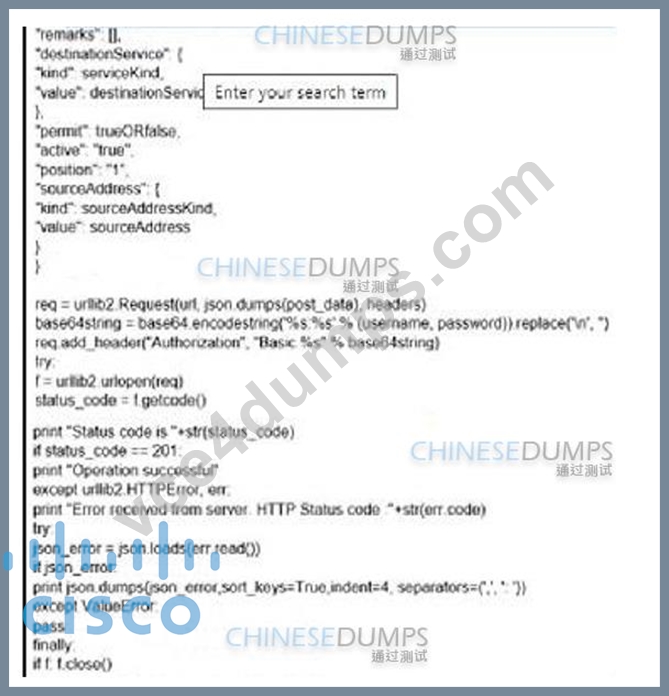
What is the function of the Python script code snippet for the Cisco ASA REST API?
- A. changes the hostname of the Cisco ASA
- B. obtains the saved configuration of the Cisco ASA firewall
- C. deletes a global rule from policies
- D. adds a global rule into policies
Answer: D
NEW QUESTION # 50
Which two configurations must be made on Cisco ISE and on Cisco TrustSec devices to force a session to be adjusted after a policy change is made? (Choose two)
- A. posture assessment
- B. aaa server radius dynamic-author
- C. tacacs-server host 10.1.1.250 key password
- D. CoA
- E. aaa authorization exec default local
Answer: B,D
NEW QUESTION # 51
Which PKI enrollment method allows the user to separate authentication and enrollment actions and also provides an option to specify HTTP/TFTP commands to perform file retrieval from the server?
- A. terminal
- B. selfsigned
- C. url
- D. profile
Answer: D
NEW QUESTION # 52
Which policy is used to capture host information on the Cisco Firepower Next Generation Intrusion Prevention System?
- A. Access Control
- B. Intrusion
- C. Network Discovery
- D. Correlation
Answer: C
Explanation:
The Firepower System uses network discovery and identity policies to collect host, application, and user data for traffic on your network. You can use certain types of discovery and identity data to build a comprehensive map of your network assets, perform forensic analysis, behavioral profiling, access control, and mitigate and respond to the vulnerabilities and exploits to which your organization is susceptible.
You can configure your network discovery policy to perform host and application detection.
Reference:
The Firepower System uses network discovery and identity policies to collect host, application, and user data for traffic on your network. You can use certain types of discovery and identity data to build a comprehensive map of your network assets, perform forensic analysis, behavioral profiling, access control, and mitigate and respond to the vulnerabilities and exploits to which your organization is susceptible.
You can configure your network discovery policy to perform host and application detection.
NEW QUESTION # 53
Refer to the exhibit.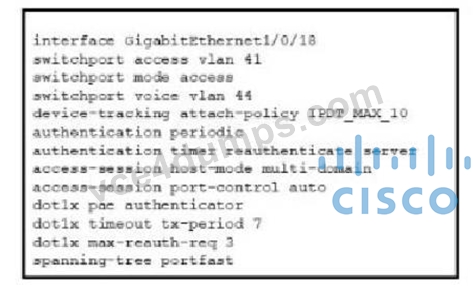
Refer to the exhibit. A Cisco ISE administrator adds a new switch to an 802.1X deployment and has difficulty with some endpoints gaining access.
Most PCs and IP phones can connect and authenticate using their machine certificate credentials. However printer and video cameras cannot base d on the interface configuration provided, what must be to get these devices on to the network using Cisco ISE for authentication and authorization while maintaining security controls?
- A. Enable insecure protocols within Cisco ISE in the allowed protocols configuration.
- B. Change the default policy in Cisco ISE to allow all devices not using machine authentication .
- C. Configure authentication event fail retry 2 action authorize vlan 41 on the interface
- D. Add mab to the interface configuration.
Answer: B
NEW QUESTION # 54
What is the result of running the crypto isakmp key ciscXXXXXXXX address 172.16.0.0 command?
- A. secures all the certificates in the IKE exchange by using the key ciscXXXXXXXX
- B. authenticates the IKEv1 peers in the 172.16.0.0/16 range by using the key ciscXXXXXXXX
- C. authenticates the IP address of the 172.16.0.0/32 peer by using the key ciscXXXXXXXX
- D. authenticates the IKEv2 peers in the 172.16.0.0/16 range by using the key ciscXXXXXXXX
Answer: D
Explanation:
Explanation The syntax of above command is: crypto isakmp key enc-type-digit keystring {address peer-address [mask] | ipv6 ipv6-address/ ipv6-prefix | hostname hostname} [no-xauth] The peer-address argument specifies the IP or IPv6 address of the remote peer. Reference: https://www.cisco.com/c/en/us/td/docs/ios-xml/ios/security/a1/sec-a1-cr-book/sec-crc4.html#wp6039879000 The syntax of above command is:
crypto isakmp key enc-type-digit keystring {address peer-address [mask] | ipv6 ipv6-address/ ipv6-prefix | hostname hostname} [no-xauth] The peer-address argument specifies the IP or IPv6 address of the remote peer.
Explanation The syntax of above command is: crypto isakmp key enc-type-digit keystring {address peer-address [mask] | ipv6 ipv6-address/ ipv6-prefix | hostname hostname} [no-xauth] The peer-address argument specifies the IP or IPv6 address of the remote peer. Reference: https://www.cisco.com/c/en/us/td/docs/ios-xml/ios/security/a1/sec-a1-cr-book/sec-crc4.html#wp6039879000
NEW QUESTION # 55
Drag and drop the exploits from the left onto the type of security vulnerability on the right.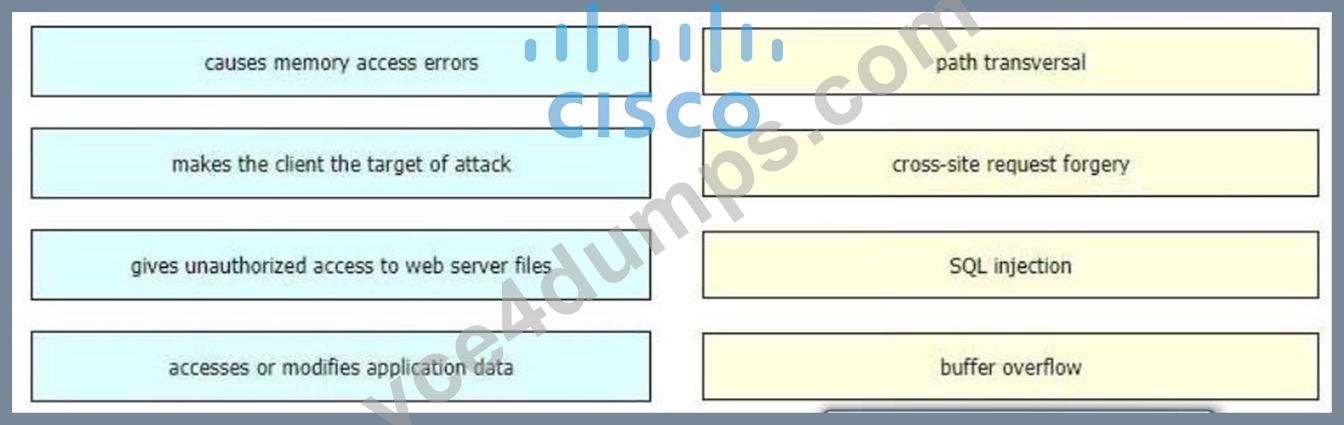
Answer:
Explanation: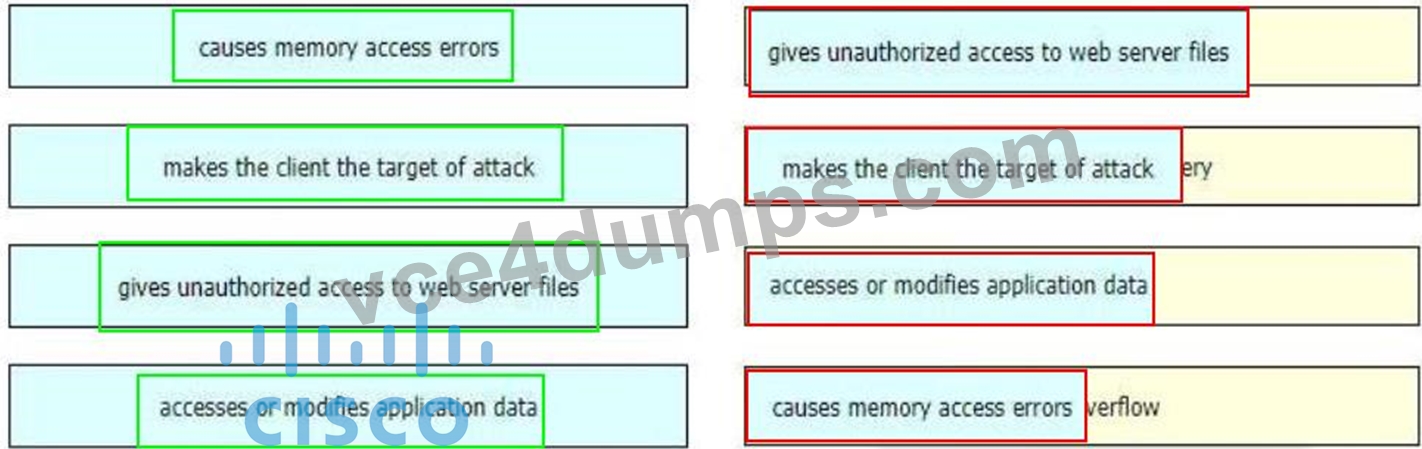
NEW QUESTION # 56
What does Cisco ISE use to collect endpoint attributes that are used in profiling?
- A. probes
- B. posture assessment
- C. Cisco AnyConnect Secure Mobility Client
- D. Cisco pxGrid
Answer: A
NEW QUESTION # 57
An organization wants to secure users, data, and applications in the cloud. The solution must be API-based and operate as a cloud-native CASB. Which solution must be used for this implementation?
- A. Cisco Cloud Email Security
- B. Cisco Firepower Next-Generation Firewall
- C. Cisco Cloudlock
- D. Cisco Umbrella
Answer: C
Explanation:
Cisco Cloudlock: Secure your cloud users, data, and applications with the cloud-native Cloud Access Security Broker (CASB) and cloud cybersecurity platform.
Cisco Cloudlock: Secure your cloud users, data, and applications with the cloud-native Cloud Access Security Broker (CASB) and cloud cybersecurity platform.
Reference:
738565.pdf
Cisco Cloudlock: Secure your cloud users, data, and applications with the cloud-native Cloud Access Security Broker (CASB) and cloud cybersecurity platform.
738565.pdf
NEW QUESTION # 58
Which role is a default guest type in Cisco ISE?
- A. Contractor
- B. Monthly
- C. Yearly
- D. Full-Time
Answer: C
NEW QUESTION # 59
Which two commands are required when configuring a flow-export action on a Cisco ASA? (Choose two.)
- A. policy-map
- B. access-list
- C. access-group
- D. flow-export event-type
- E. flow-export template timeout-rate 15
Answer: A,D
NEW QUESTION # 60
Refer to the exhibit. An administrator is adding a new Cisco FTD device to their network and wants to manage it with Cisco FMC. The Cisco FTD uses a registration key of Cisc392368270 and is not behind a NAT device, Which command is needed to enable this on the Cisco FTD?
- A. configure manager add <FMC IP address> <registration key>
- B. configure manager add <FMC IP address> <registration key> 16
- C. configure manager add DONTRESOLVE kregistration key>
- D. configure manager add DONTRESOLVE <registration key> FTD123
Answer: A
NEW QUESTION # 61
Which public cloud provider supports the Cisco Next Generation Firewall Virtual?
- A. Google Cloud Platform
- B. Red Hat Enterprise Visualization
- C. VMware ESXi
- D. Amazon Web Services
Answer: D
Explanation:
Cisco Firepower NGFW Virtual (NGFWv) is the virtualized version of Cisco's Firepower next generation firewall. The Cisco NGFW virtual appliance is available in the AWS and Azure marketplaces. In AWS, it can be deployed in routed and passive modes. Passive mode design requires ERSPAN, the Encapsulated Remote Switched Port Analyzer, which is currently not available in Azure. In passive mode, NGFWv inspects packets like an Intrusion Detection System (IDS) appliance, but no action can be taken on the packet. In routed mode NGFWv acts as a next hop for workloads. It can inspect packets and also take action on the packet based on rule and policy definitions. Reference: https://www.cisco.com/c/en/us/products/collateral/security/adaptive-security-virtual-appliance-asav/ white-paper-c11-740505.html The Cisco NGFW virtual appliance is available in the AWS and Azure marketplaces. In AWS, it can be deployed in routed and passive modes. Passive mode design requires ERSPAN, the Encapsulated Remote Switched Port Analyzer, which is currently not available in Azure.
In passive mode, NGFWv inspects packets like an Intrusion Detection System (IDS) appliance, but no action can be taken on the packet.
In routed mode NGFWv acts as a next hop for workloads. It can inspect packets and also take action on the packet based on rule and policy definitions.
Cisco Firepower NGFW Virtual (NGFWv) is the virtualized version of Cisco's Firepower next generation firewall. The Cisco NGFW virtual appliance is available in the AWS and Azure marketplaces. In AWS, it can be deployed in routed and passive modes. Passive mode design requires ERSPAN, the Encapsulated Remote Switched Port Analyzer, which is currently not available in Azure. In passive mode, NGFWv inspects packets like an Intrusion Detection System (IDS) appliance, but no action can be taken on the packet. In routed mode NGFWv acts as a next hop for workloads. It can inspect packets and also take action on the packet based on rule and policy definitions. Reference: https://www.cisco.com/c/en/us/products/collateral/security/adaptive-security-virtual-appliance-asav/ white-paper-c11-740505.html
NEW QUESTION # 62
An organization has a Cisco ESA set up with policies and would like to customize the action assigned for violations. The organization wants a copy of the message to be delivered with a message added to flag it as a DLP violation. Which actions must be performed in order to provide this capability?
- A. deliver and add disclaimer text
- B. quarantine and alter the subject header with a DLP violation
- C. deliver and send copies to other recipients
- D. quarantine and send a DLP violation notification
Answer: A
Explanation:
You specify primary and secondary actions that the appliance will take when it detects a possible DLP violation in an outgoing message. Different actions can be assigned for different violation types and severities.
Primary actions include:
- Deliver
- Drop
- Quarantine
Secondary actions include:
- Sending a copy to a policy quarantine if you choose to deliver the message. The copy is a perfect clone of the original, including the Message ID. Quarantining a copy allows you to test the DLP system before deployment in addition to providing another way to monitor DLP violations. When you release the copy from the quarantine, the appliance delivers the copy to the recipient, who will have already received the original message.
- Encrypting messages. The appliance only encrypts the message body. It does not encrypt the message headers.
- Altering the subject header of messages containing a DLP violation.
- Adding disclaimer text to messages.
- Sending messages to an alternate destination mailhost.
- Sending copies (bcc) of messages to other recipients. (For example, you could copy messages with critical DLP violations to a compliance officer's mailbox for examination.)
- Sending a DLP violation notification message to the sender or other contacts, such as a manager or DLP compliance officer.
Reference:
b_ESA_Admin_Guide_12_0/b_ESA_Admin_Guide_chapter_010001.html
b_ESA_Admin_Guide_12_0/b_ESA_Admin_Guide_chapter_010001.html
NEW QUESTION # 63
What is the purpose of the Cisco Endpoint loC feature?
- A. It provides stealth threat prevention.
- B. It provides precompromise detection.
- C. lt is an incident response tool 6W
- D. lt is a signature-based engine. W
Answer: C
Explanation:
https://www.cisco.com/c/dam/en_us/about/doing_business/legal/service_descriptions/docs/Cisco_Secure_Managed_Endpoint.pdf
NEW QUESTION # 64
What is provided by the Secure Hash Algorithm in a VPN?
- A. authentication
- B. key exchange
- C. encryption
- D. integrity
Answer: D
Explanation:
Explanation The HMAC-SHA-1-96 (also known as HMAC-SHA-1) encryption technique is used by IPSec to ensure that a message has not been altered. (-> Therefore answer "integrity" is the best choice). HMAC-SHA-1 uses the SHA-1 specified in FIPS-190-1, combined with HMAC (as per RFC 2104), and is described in RFC 2404. Reference: https://www.ciscopress.com/articles/article.asp?p=24833&seqNum=4 The HMAC-SHA-1-96 (also known as HMAC-SHA-1) encryption technique is used by IPSec to ensure that a message has not been altered. (-> Therefore answer "integrity" is the best choice). HMAC-SHA-1 uses the SHA-1 specified in FIPS-190-1, combined with HMAC (as per RFC 2104), and is described in RFC 2404.
Explanation The HMAC-SHA-1-96 (also known as HMAC-SHA-1) encryption technique is used by IPSec to ensure that a message has not been altered. (-> Therefore answer "integrity" is the best choice). HMAC-SHA-1 uses the SHA-1 specified in FIPS-190-1, combined with HMAC (as per RFC 2104), and is described in RFC 2404. Reference: https://www.ciscopress.com/articles/article.asp?p=24833&seqNum=4
NEW QUESTION # 65
What provides total management for mobile and PC including managing inventory and device tracking, remote view, and live troubleshooting using the included native remote desktop support?
- A. mobile access management
- B. mobile content management
- C. mobile device management
- D. mobile application management
Answer: C
NEW QUESTION # 66
......
Cisco 350-701 exam is one of the most challenging exams in the IT industry. It requires extensive knowledge of network security, cloud computing, and cybersecurity. It is recommended that candidates have at least three to five years of experience in the IT industry before attempting 350-701 exam to have a solid understanding of the concepts covered in the exam. 350-701 exam consists of multiple-choice questions, drag and drop, and simulation questions.
New 350-701 exam dumps Use Updated Cisco Exam: https://www.vce4dumps.com/350-701-valid-torrent.html
Verified 350-701 Dumps Q&As - 350-701 Test Engine with Correct Answers: https://drive.google.com/open?id=1Wluorc6ml2HyzT6Sqaq9b1th93MClKT5