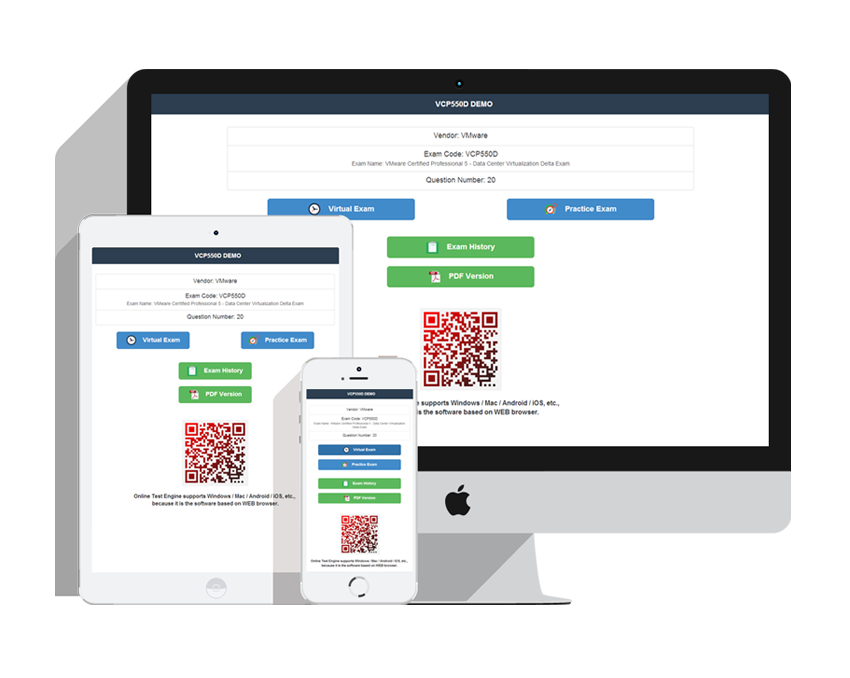
Free Demo


ISC2 HCISPP Exam Certification Details:
| Exam Name | ISC2 Certified HealthCare Information Security and Privacy Practitioner (HCISPP) |
| Number of Questions | 125 |
| Exam Price | $599 (USD) |
| Passing Score | 700 / 1000 |
| Duration | 180 mins |
| Sample Questions | ISC2 HCISPP Sample Questions |
| Schedule Exam | Pearson VUE |
| Exam Code | HCISPP |
Do you want to enter into the big international companies? Do you want to meet influential people and extraordinary people of IT field? Do you want to make some achievements in your career? Getting the HCISPP certification may be the first step for you. As the major exam of ISC, ISC are recognized by most companies and it proves your IT ability. But the problem is how to get ISC certification quickly. It will be twice as much as can be accomplished with half of effort with a good helper. VCE4Dumps will be a good helper in the course of preparing your HCISPP test dumps. You just need to spend your spare time to practice the HCISPP vce files and HCISPP test dumps, the test wll be easy for you.

Why you choose VCE4Dumps
First, it is professional. HCISPP exam dumps vce and HCISPP dumps pdf are created by our IT workers who are specialized in the study of real HCISPP test dumps for many years and they check the updating of HCISPP vce dumps everyday to make sure the valid of HCISPP dumps latest, so you can rest assure of the accuracy of our HCISPP vce dumps. The HCISPP vce files of our VCE4Dumps contain questions and correct answers and detailed answer explanations and analysis, which apply to any level of candidates. You will pass the test with high rate If you practice the HCISPP dumps latest seriously and skillfully.
Second, the pass rate is high. May be you are still wonder how to choose, we can show you the date of our pass rate in recent years. The HCISPP exam dumps vce helped more than 100000+ candidates to get the certification and the pass rate is up to 79%. Many customers of VCE4Dumps reflected that our HCISPP vce dumps have 80% similarity to the real HCISPP test dumps. So if you prepare the HCISPP dumps pdf and HCISPP dumps latest seriously and remember the key points of HCISPP test dumps, your pass rate will reach to 80%. So you need to pay much attention to the HCISPP exam dumps vce before test.
Third, it is convenient. Online test engine is only service you can enjoy from our website. It is a simulation of formal test and you can feel the atmosphere of real test. What's more, it allows you to practice the HCISPP dumps pdf in any electronic equipments. If you open it with internet, you can do the HCISPP vce files anywhere. When you are waiting people or taking a bus, you can remember or practice the HCISPP vce files without any limitation.
The service of VCE4Dumps
First, you can download the trial of HCISPP free vce before you buy.
Second, you will be allowed to free updating the HCISPP exam dumps vce one-year after you become a member of us.
Third, we offer 24/7 customer assisting to support if you have any problems about the downloading or purchasing the HCISPP vce dumps.
Forth, we adhere to the principle of No help, Full refund. The money will be full refund if you got a bad result with our HCISPP test dumps.
ISC2 HCISPP Exam Syllabus Topics:
| Topic | Details |
|---|---|
Healthcare Industry (12%) | |
| Understand the Healthcare Environment Components | - Types of Organizations in the Healthcare Sector (e.g., providers, pharma, payers) - Health Insurance (e.g., claims processing, payment models, health exchanges, clearing houses) - Coding (e.g., Systematized Nomenclature of Medicine Clinical Terms (SNOMED CT), International Classification of Diseases (ICD) 10) - Revenue Cycle (i.e., billing, payment, reimbursement) - Workflow Management - Regulatory Environment - Public Health Reporting - Clinical Research (e.g., processes) - Healthcare Records Management |
| Understand Third-Party Relationships | - Vendors - Business Partners - Regulators - Other Third-Party Relationships |
| Understand Foundational Health Data Management Concepts | - Information Flow and Life Cycle in the Healthcare Environments - Health Data Characterization (e.g., classification, taxonomy, analytics) - Data Interoperability and Exchange (e.g., Health Level 7 (HL7), International Health Exchange (IHE), Digital Imaging and Communications in Medicine (DICOM)) - Legal Medical Records |
Information Governance in Healthcare (5%) | |
| Understand Information Governance Frameworks | - Security Governance (e.g., charters, roles, responsibilities) - Privacy Governance (e.g., charters, roles, responsibilities) |
| Identify Information Governance Roles and Responsibilities | |
| Align Information Security and Privacy Policies, Standards and Procedures | - Policies - Standards - Processes and Procedures |
| Understand and Comply with Code of Conduct/Ethics in a Healthcare Information Environment | - Organizational Code of Ethics - (ISC)² Code of Ethics |
Information Technologies in Healthcare (8%) | |
| Understand the Impact of Healthcare Information Technologies on Privacy and Security | - Increased Exposure Affecting Confidentiality, Integrity and Availability (e.g., threat landscape) - Oversight and Regulatory Challenges - Interoperability - Information Technologies |
| Understand Data Life Cycle Management (e.g., create, store, use, share, archive, destroy) | |
| Understand Third-Party Connectivity | - Trust Models for Third-Party Interconnections - Technical Standards (e.g., physical, logical, network connectivity) - Connection Agreements (e.g., Memorandum of Understanding (MOU), Interconnection Security Agreements (ISAs)) |
Regulatory and Standards Environment (15%) | |
| Identify Regulatory Requirements | - Legal Issues that Pertain to Information Security and Privacy for Healthcare Organizations - Data Breach Regulations - Protected Personal and Health Information (e.g., Personally Identifiable Information (PII), Personal Health Information (PHI)) - Jurisdiction Implications - Data Subjects - Research |
| Recognize Regulations and Controls of Various Countries | - Treaties - Laws and Regulations (e.g., European Union (EU) Data Protection Directive, Health Insurance Portability and Accountability Act /Health Information Technology for Economic and Clinical Health (HIPAA/HITECH), General Data Protection Regulation (GDPR), Personal Information Protection and Electronic Documents Act (PIPEDA)) |
| Understand Compliance Frameworks | - Privacy Frameworks (e.g., Organization for Economic Cooperation and Development (OECD) Privacy principles, Asia-Pacific Economic Cooperation (APEC), Generally Accepted Privacy Principles (GAPP)) - Security Frameworks (e.g., International Organization for Standardization (ISO), National Institute of Standards and Technology (NIST), Common Criteria (CC)) |
Privacy and Security in Healthcare (25%) | |
| Understand Security Objectives/Attributes | - Confidentiality - Integrity - Availability |
| Understand General Security Definitions and Concepts | - Identity and Access Management (IAM) - Data Encryption - Training and Awareness - Logging, Monitoring and Auditing - Vulnerability Management - Segregation of Duties - Least Privilege (Need to Know) - Business Continuity (BC) - Disaster Recovery (DR) - System Backup and Recovery |
| Understand General Privacy Definitions and Concepts | - Consent/Choice - Limited Collection/Legitimate Purpose/Purpose Specification - Disclosure Limitation/Transfer to Third-Parties/ Trans-border Concerns - Access Limitation - Accuracy, Completeness and Quality - Management, Designation of Privacy Officer, Supervisor Re-authority, Processing Authorization and Accountability - Training and Awareness - Transparency and Openness (e.g., notice of privacy practices) - Proportionality, Use and Disclosure, and Use Limitation - Access and Individual Participation - Notice and Purpose Specification - Events, Incidents and Breaches |
| Understand the Relationship Between Privacy and Security | - Dependency - Integration |
| Understand Sensitive Data and Handling | - Sensitivity Mitigation (e.g., de-identification, anonymization) - Categories of Sensitive Data (e.g., behavioral health) |
Risk Management and Risk Assessment (20%) | |
| Understand Enterprise Risk Management | - Information Asset Identification - Asset Valuation - Exposure - Likelihood - Impact - Threats - Vulnerability - Risk - Controls - Residual Risk - Acceptance |
| Understand Information Risk Management Framework (RMF) (e.g., International Organization for Standardization (ISO), National Institute of Standards and Technology (NIST)) | |
| Understand Risk Management Process | - Definition - Approach (e.g., qualitative, quantitative) - Intent - Life Cycle/Continuous Monitoring - Tools/Resources/Techniques - Desired Outcomes - Role of Internal and External Audit/Assessment |
| Identify Control Assessment Procedures Utilizing Organization Risk Frameworks | |
| Participate in Risk Assessment Consistent with the Role in Organization | - Information Gathering - Risk Assessment Estimated Timeline - Gap Analysis |
| Understand Risk Response (e.g., corrective action plan) | - Mitigating Actions - Avoidance - Transfer - Acceptance - Communications and Reporting |
| Utilize Controls to Remediate Risk (e.g., preventative, detective, corrective) | - Administrative - Physical - Technical |
| Participate in Continuous Monitoring | |
Third-Party Risk Management (15%) | |
| Understand the Definition of Third-Parties in Healthcare Context | |
| Maintain a List of Third-Party Organizations | - Third-Party Role/Relationship with the Organization - Health Information Use (e.g., processing, storage, transmission) |
| Apply Management Standards and Practices for Engaging Third-Parties | - Relationship Management |
| Determine When a Third-Party Assessment Is Required | - Organizational Standards - Triggers of a Third-Party Assessment |
| Support Third-Party Assessments and Audits | - Information Asset Protection Controls - Compliance with Information Asset Protection Controls - Communication of Results |
| Participate in Third-Party Remediation Efforts | - Risk Management Activities - Risk Treatment Identification - Corrective Action Plans - Compliance Activities Documentation |
| Respond to Notifications of Security/Privacy Events | - Internal Processes for Incident Response - Relationship Between Organization and Third-Party Incident Response - Breach Recognition, Notification and Initial Response |
| Respond to Third-Party Requests Regarding Privacy/Security Events | - Organizational Breach Notification Rules - Organizational Information Dissemination Policies and Standards - Risk Assessment Activities - Chain of Custody Principles |
| Promote Awareness of Third-Party Requirements | - Information Flow Mapping and Scope - Data Sensitivity and Classification - Privacy and Security Requirements - Risks Associated with Third-Parties |
Reference: https://www.isc2.org/Certifications/HCISPP